Attended Support Guide
Interactive session management requiring end-user interaction and on-screen verification.
Standard operating procedures and authorization boundaries governing user-attended interventions, automated background servicing, and context-aware device validation.
Remote system operations require distinct operational states tailored to endpoint custody, security verification levels, and technician presence. Differentiating between user-present troubleshooting and automated scheduled servicing ensures baseline security compliance while preventing operational lockouts.
Our operational matrix categorizes access into monitored attended interactions, secured unattended execution windows, and contextual trust evaluations based on device health and network provenance.
Configuring granular permissions across corporate infrastructure ensures zero privilege creep and rigorous auditing.
100% End-to-End Cryptographic Validation.
Interactive session management requiring end-user interaction and on-screen verification.
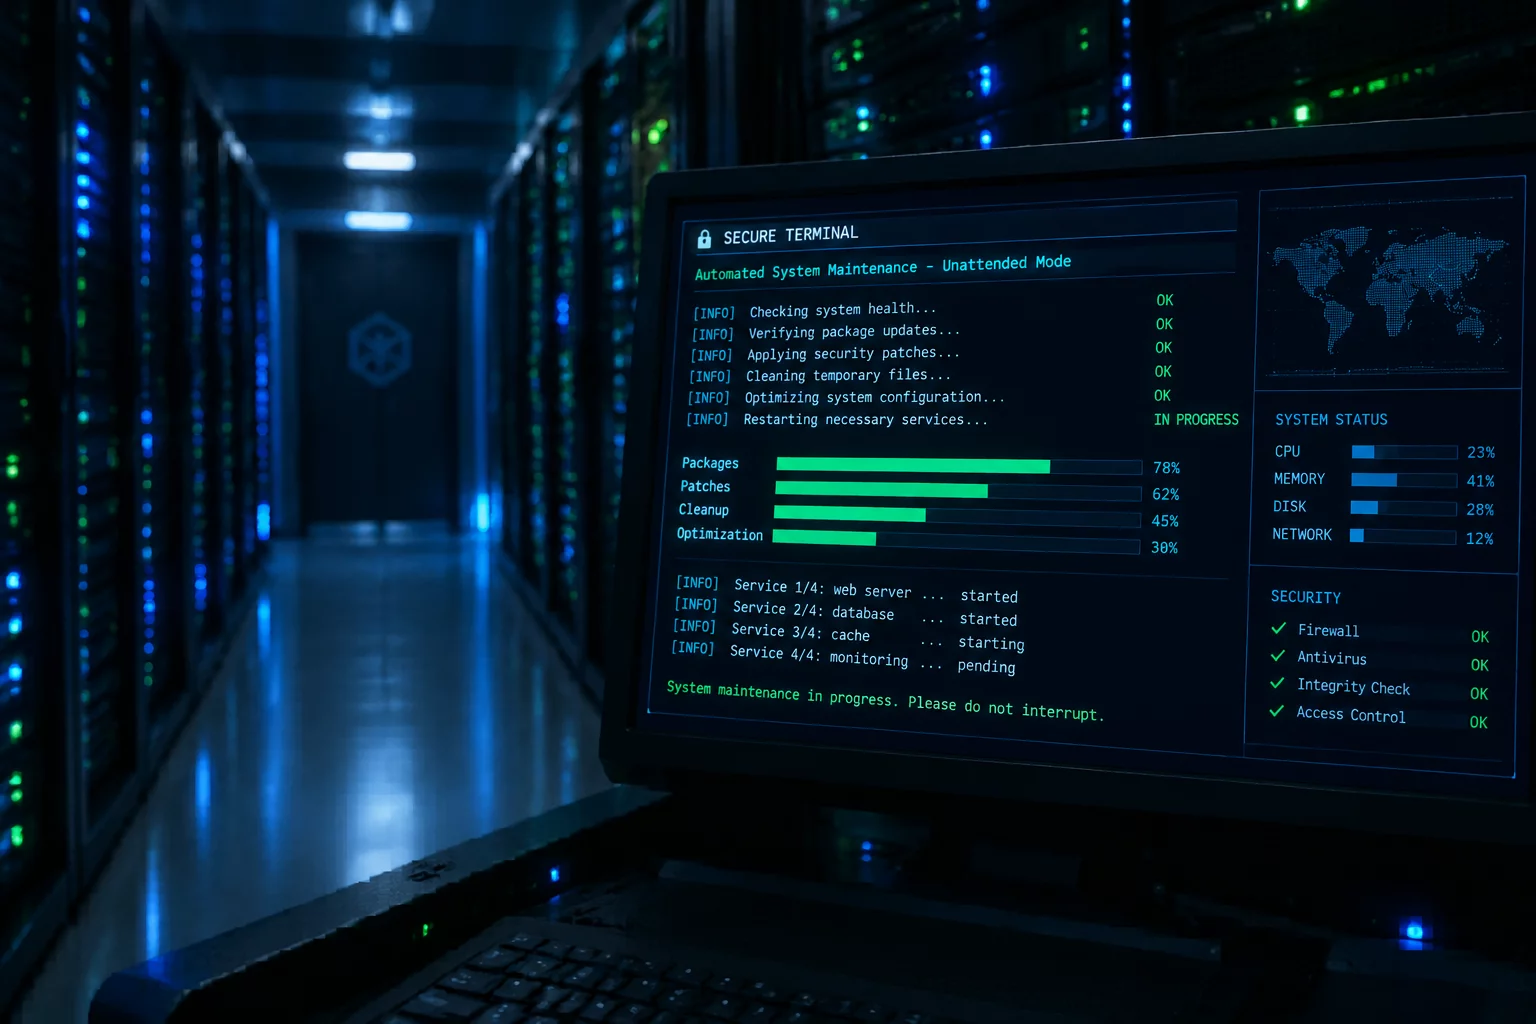
Scheduled background services and unattended infrastructure management workflows.
Hardware telemetry, security posture validation, and zero-trust perimeter integration.